Fake IT Support Calls: When "the Helpdesk" Rings You
A friendly caller from "IT" says there is a problem with your account and walks you through fixing it. Here is how helpdesk impersonation works, why it succeeds, and the rules that stop it.

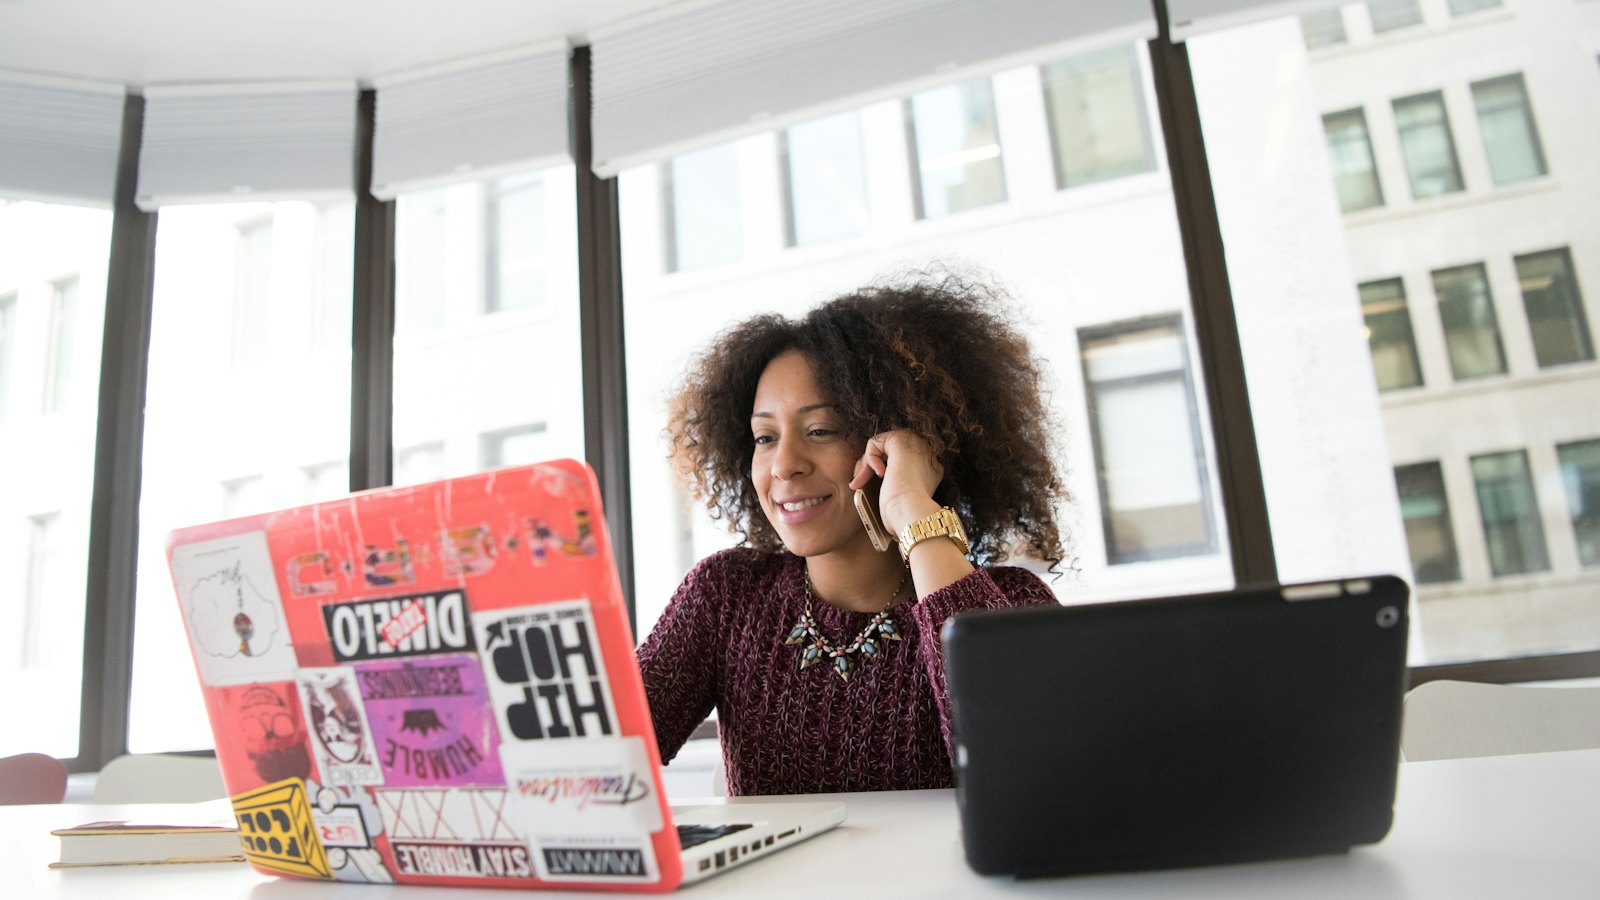
The phone rings. The caller is polite, knows your name and your manager's name, and says they are from IT. There is a problem with your account, or a security update that needs installing, and they will talk you through it. It will only take two minutes.
This is one of the oldest attacks there is, and it still works, because helping IT feels like the responsible thing to do.
How the call usually goes
- Research first. The caller gathers names, job titles and the name of your IT provider from the company website, social media and earlier emails.
- A plausible problem. Your mailbox is full, your account has been flagged, your laptop is missing an update, or suspicious activity has been detected.
- The ask. Read out a code you just received. Approve a sign-in prompt. Visit a website and install a small tool so they can "take a look". Tell them your password "so we can reset it".
- Reassurance. If you hesitate, they are patient, even a little hurt. They are only trying to help, and your manager wanted this fixed today.
The remote access trap: once you install a remote access tool for a caller, they can see your screen and control your computer, including anything you are signed in to. Genuine support staff will tell you in advance how they work; they will not cold-call you and ask you to install something new.
Why it works
It uses authority (IT is in charge of the systems), helpfulness (you want to cooperate), fear (something is wrong with your account) and a little embarrassment, because many people feel unsure about technology and are glad someone else is taking charge.
Rules every employee should know
- IT will never ask for your password. Not by phone, email or chat. Ever.
- Never read out a code sent to your phone or approve a sign-in you did not start.
- Do not install anything because a caller asked you to.
- Hang up and call back on the helpdesk number you already have, from your intranet or a previous ticket, not a number the caller gives you.
- Report the call to your security team, even if you did nothing wrong. Others are probably being called too.
For IT teams: publish how genuine support works, for example "we will always give you a ticket number" or "we never phone you first about passwords", so employees have a simple test to apply. And make sure your own helpdesk verifies callers properly before resetting passwords, because attackers also call the helpdesk pretending to be staff.
If you think you have been caught
Disconnect your computer from the network, change your password from another device, and tell your IT or security team straight away what you shared or installed. The sooner they know, the sooner they can close the door.
Practising the pause
The best defence is a reflex: pause, hang up, call back. CyberWatch AI's training lessons cover phone and impersonation attacks alongside email, and its reporting feature gives employees one simple place to flag anything suspicious so the security team sees a pattern early.